Why Next-Gen BNG Models Are the Secret to Scalable ISP Growth
Centralised, virtualised, disaggregated and edge BNG models compared, and why subscriber management usually decides the outcome rather than forwarding.
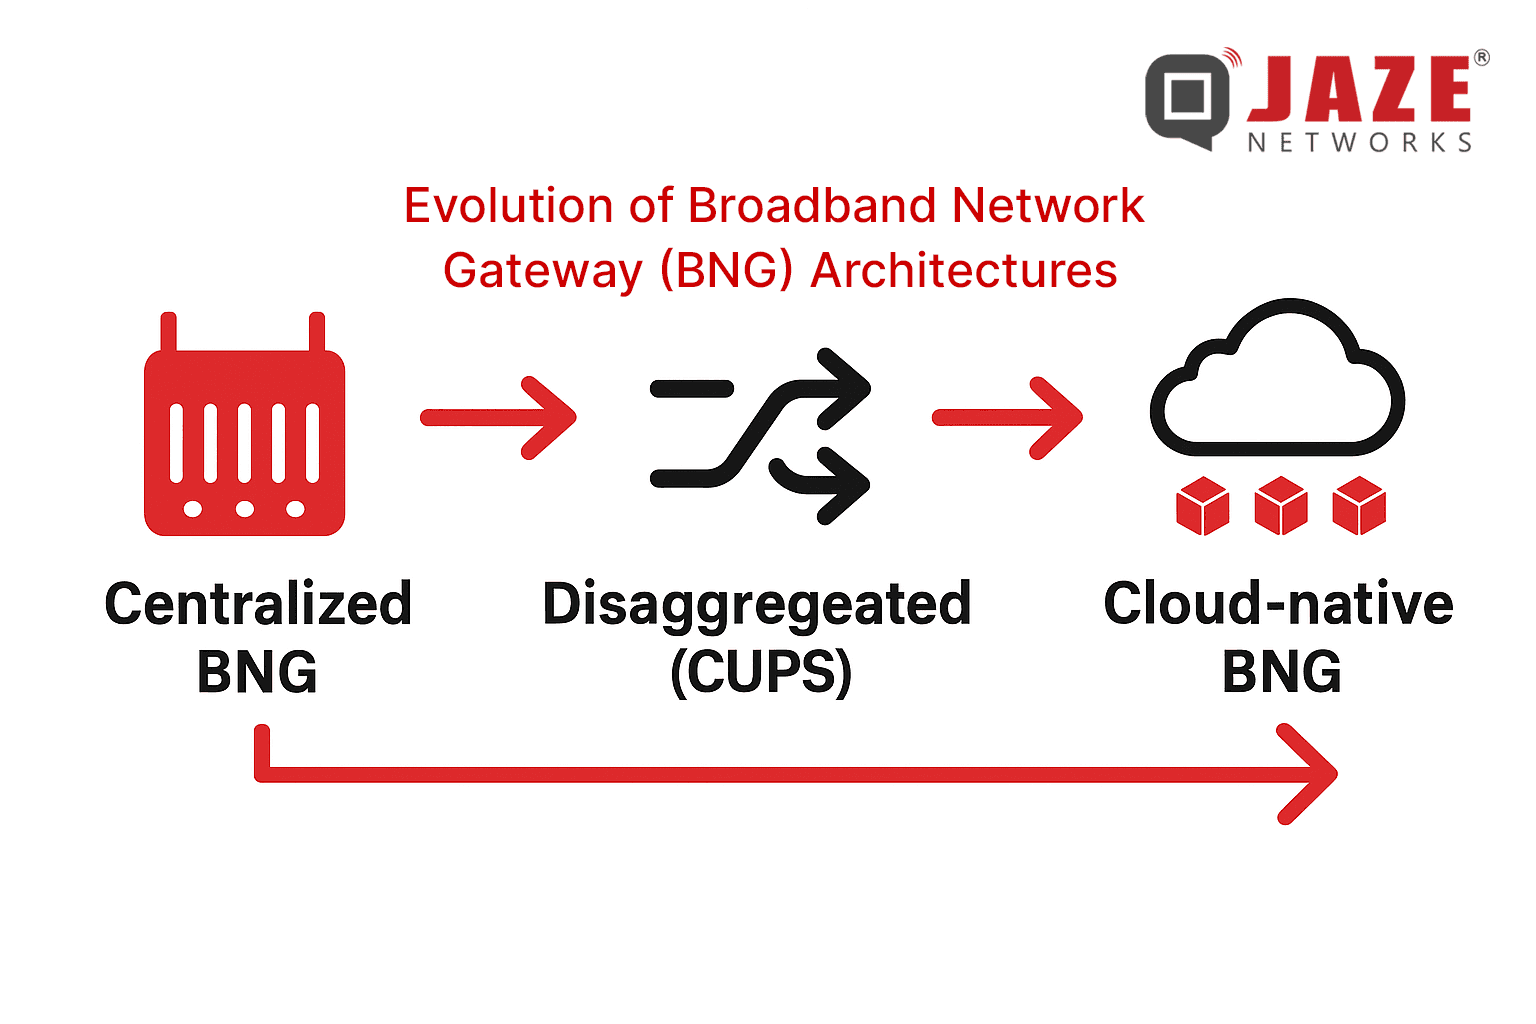
The Broadband Network Gateway used to be a fairly contained piece of the network: terminate subscriber sessions, aggregate access traffic, forward it on. It has since become the point where subscriber state, policy enforcement and service delivery all meet, which makes how it is built a question worth revisiting.
Why the traditional model is under strain
Older deployments share a shape. A monolithic appliance terminates PPPoE or IPoE sessions, control and forwarding live together in the same box, and the box sits at an aggregation site chosen for traffic patterns that no longer apply.
Several things have changed underneath that design:
- Subscriber counts and per-subscriber traffic have both risen substantially, and streaming and remote work made the load steadier rather than peakier
- Access has diversified. Fibre, fixed wireless and newer Wi-Fi generations all arrive at the same platform expecting the same policy treatment
- Capacity has to be added in smaller increments than a chassis upgrade allows
- Distributed services and edge computing want forwarding closer to the subscriber than a central aggregation point provides
The models available
Centralised hardware. The classic arrangement, with control and user plane together in a purpose-built appliance. Predictable and well understood, with performance that is easy to reason about. Less easy to scale in small steps, and slower to accommodate a new access type.
Virtualised. BNG functions run as software on commodity hardware. Capacity grows in smaller increments, upgrades become a software exercise, and orchestration starts to matter as much as the data path. The trade is that performance now depends on tuning that the appliance previously handled.
Disaggregated, with control and user plane separated. Session state and policy sit in one place while forwarding sits in another. The user plane can move toward the edge to cut latency and backhaul, while the control plane stays central and scales independently. This is what makes converged fixed and wireless access practical under a single policy regime.
Distributed at the edge. Forwarding pushed out to edge or aggregation nodes, with multiple access types held under one control system. It suits operators whose footprint is geographically spread or whose traffic is increasingly local.
What actually decides the outcome
The architecture gets the attention, but the constraint is usually subscriber management rather than packet forwarding. Separating the planes means session state has to stay coherent across more components than before. A subscriber authenticating at the edge, being assigned policy centrally and having usage recorded somewhere else again is a data consistency problem as much as a networking one.
That places weight on the surrounding systems: RADIUS or Diameter that can carry the session volume, policy definitions applied identically regardless of where a subscriber attaches, accounting that stays accurate when the user plane moves, and provisioning that does not assume a fixed topology.
An operator evaluating a change here is well advised to look at what the management layer can represent before choosing the network design, because a disaggregated BNG governed by a platform that assumes one appliance per site tends to reproduce the old constraints in a more complicated form.
Jaze ISP Manager handles authentication and policy in a vendor-agnostic way, applying subscriber policy through each vendor's own attributes, so the access architecture can change without the subscriber management layer having to be rebuilt around it.